Tesla Motors pwned.
by admin
Saturday, April 25th, 2015 at 4:26 pm
http://teslamotors.com and their twitter got owned today
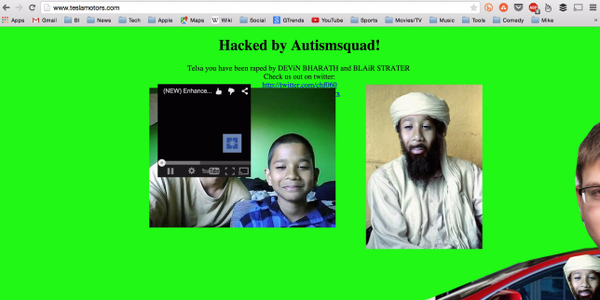
whoever had control of the twitter mistakenly posted a screenshot of their skype session
the site is currently down.
http://teslamotors.com and their twitter got owned today
whoever had control of the twitter mistakenly posted a screenshot of their skype session
the site is currently down.
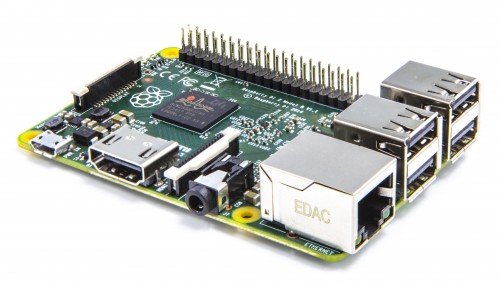
cyberkryption has finished getting a build for Kali Linux 1.1.10 for a Raspberry Pi 2 with working XFCE and raspi-config
Check out his blog for more info: cyberkryption.wordpress.com

ATT U-Verse service includes the VAP2500 video access point as part of the installation,. From their guide “The VAP2500 enables you to transmit multiple standard- and high-definition video streams throughout your home wirelessly. You can enjoy a full range of video services and applications without having to run wires, lay cables, or drill holes. The U-verse Wireless Access Point operates only with authorized U-verse Wireless
Receiver(s).” Apparently it’s full of holes too:
1. Readable plain-text file, admin.conf, which holds the username and md5 encrypted passwords
(defaults are: ATTadmin : 1b12957d189cde9cda68e1587c6cfbdd MD5 : 2500!VaP
super : 71a5ea180dcd392aabe93f11237ba8a9 MD5 : M0torola!)
2. They use the md5 hash of the username as a cookie for authentication
3. gui suppports command injection
More info: http://goto.fail
similar report: http://www.dslreports.com
Analysis and demo written by @0x710DDDD http://www.secniu.com/cve-2014-1767-afd-sys-double-free-vulnerability-analysis-and-exploit/
Quick and dirty Metasploit module based off of @yuange ‘s code from 2009. This vulnerability affects Windows 95 IE 3.0 until Windows 10 IE 11. https://forsec.nl/2014/11/cve-2014-6332-internet-explorer-msf-module/ Module here: ms14_064_ie_olerce.rb
This module exploits a vulnerability found in Windows Object Linking and Embedding (OLE) allowing arbitrary code execution, publicly exploited in the wild as MS14-060 patch bypass.
The Microsoft update tried to fix the vulnerability publicly known as “Sandworm”. Platforms such as Windows Vista SP2 all the way to Windows 8, Windows Server 2008 and 2012 are known to be vulnerable.
http://www.exploit-db.com/exploits/35236/
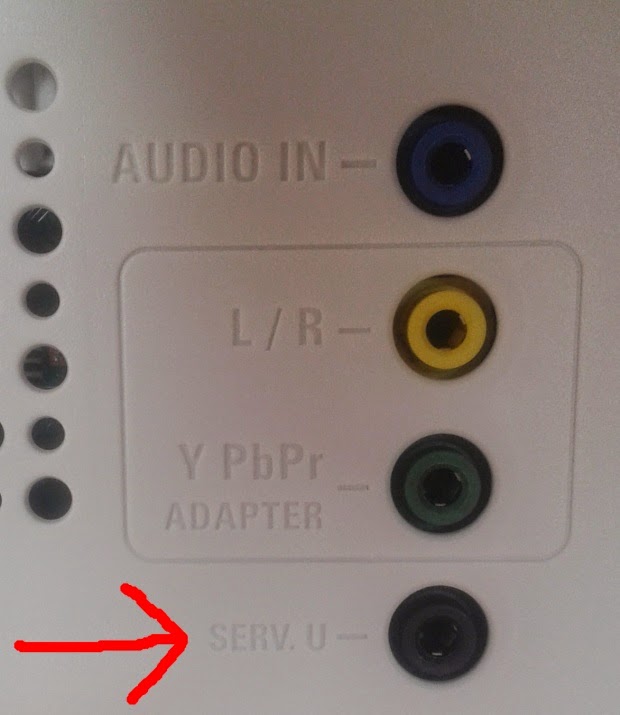
Using a remote stack overflow in libupnp Fred was able to take control of his TV using the serial port in the back of the TV http://www.fredericb.info/2014/11/exploitation-of-philips-smart-tv.html
DPAPIck is a forensic tool to deal, in an offline way, with Microsoft Windows® protected data, using the DPAPI (Data Protection API). The tool was updated to support Windows versions all the way to 8.1.
list of recoverable secrets are :
Src: dpapick.com
http://rcrypt.0xrage.com/
Upload your executable file to encrypt and pack it. So far supports rcrypt,fsg,upx,mew,upolyx,petite, & afx pecrypt.
Quickly find and explore shares our current user has access to: https://www.veil-framework.com/hunting-sensitive-data-veil-framework/


We love our country, but fear our government.
 Skype
 Email
 Keybase.io


